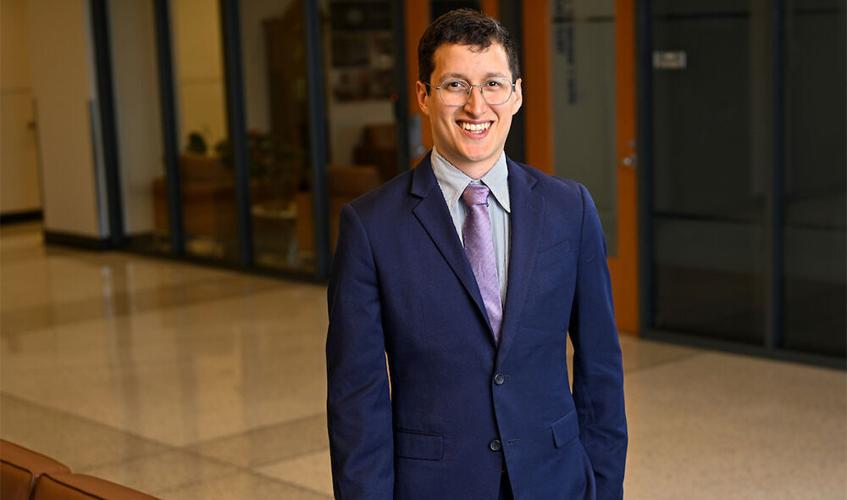
Harbert College of Business faculty member's recent research is first step toward tracing security vulnerabilities to better protect businesses and consumers using open-source AI software
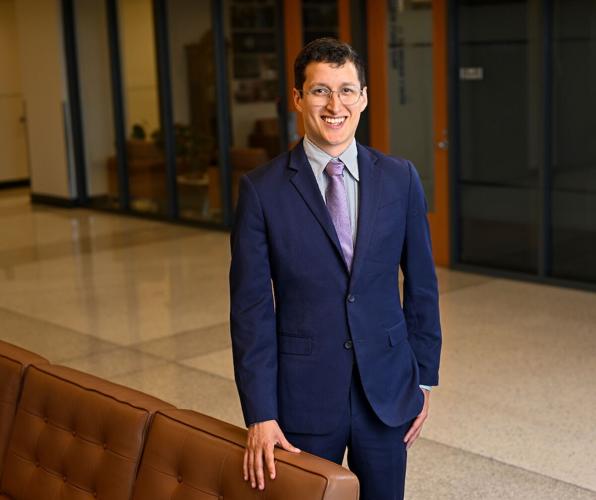
Several years ago, when Ben Lazarine was a master’s student, he was probing the software developer platform Github to try to understand how open-source software was being shared and adapted. He was studying cybersecurity and hypothesized that open-source software presents security vulnerabilities that can be easily passed from one project to another. But Lazarine was struggling to find how all of the projects were borrowing and sharing software to test this.
On platforms like Github, developers often use a mechanism called “forking” to make a copy of a project and develop it, making it traceable to the original source. One could map the connections into a giant networking tree. But when developers use a project without forking, it becomes untraceable over time.
People are also reading…
Instead of one tree, “you end up with a whole bunch of trees in your forest, and none of them are connected whatsoever,” Lazarine said. “You end up with a lot of very boring networks when you’re trying to ask interesting research questions.”
Lazarine, who went on to earn a Ph.D. and is now an assistant professor in the Department of Business Analytics and Information Systems, decided to use machine learning to come up with another way to find these connections, specifically focused on AI projects, which are frequently built on layers of open-source software.
In a research paper published in the Journal of Management Information Systems, Lazarine and his co-authors laid out their AI-enabled framework that allowed them to predict connections between AI projects that were not forked with 96% precision. It’s the first step toward tracing security vulnerabilities to better protect businesses and consumers who end up using the AI software.
“The main takeaway is that it highlights the vulnerability spread that is going on within the community from previous projects to brand new AI development,” Lazarine said. “If we don’t take care of this and figure it out, as we continue to develop AI, it’s just going to continue to be built on top of insecure code. It creates a snowball effect.”
Lazarine was surprised to find the main spreaders of vulnerabilities were not always the most popular software that was being copied frequently, but rather less popular ones that were being discreetly copied. Without the AI mechanism that he and his collaborators developed, these spreaders would likely have been overlooked.
As AI grows in popularity, Lazarine’s research has implications for businesses that are jumping on new tools and platforms. In the excitement to adapt to the age of AI, companies may be missing cybersecurity threats. Lazarine plans to focus his future research on how organizations can become more aware of where they’re adopting their technologies from and the security implications of those decisions. He’s also looking into ways to patch up vulnerabilities in security codes in existing projects.
More immediately, he’s working on a project now that can offer organizations a more secure application to use if they’re looking at using vulnerable ones.
“I’m trying to make this as actionable as possible for people,” Lazarine said. “It’s something people need to be thinking about when they’re adopting open-source technologies into their workflows.”
While most organizations will need to pay more attention to cybersecurity threats in the age of AI, Lazarine hopes his research will ultimately alleviate the burden of having to do all the detective work themselves.
“People want to use technology that’s going to make their jobs more exciting or easier,” Lazarine said. “We want to help people focus on the cool stuff and then remove some of the cybersecurity burden at the same time.”
Lazarine conducted this research with Indiana University faculty Sagar Samtani and Ramesh Venkataraman and University of Texas at San Antonio faculty member Hongyi Zhu. Their paper is titled “Protecting the linked artificial intelligence repositories on open source software platforms: A graph self-supervised learning approach.”